Important technology news and analysis focused on AI, cybersecurity, software, digital privacy, automation, and business technology trends.
CISA added PaperCut NG/MF CVE-2026-81578 and CVE-2026-82078 to KEV on August 31, 2026. Here is who is affected, how the chain works, and what small businesses should do before the September 14 due date.
CISA added CVE-2026-64849, an MLflow SSRF issue, to KEV. Here is the practical small-business checklist for AI infrastructure owners.
CISA added Ray CVE-2025-62593 to the Known Exploited Vulnerabilities catalog. Here is what small businesses should check across AI compute, developer tools, and Ray dashboards.
Atlassian fixed one Rovo prompt-injection flaw, but the bigger lesson is AI assistant governance. Here is what small businesses using Jira, Confluence, and connected SaaS tools should review now.
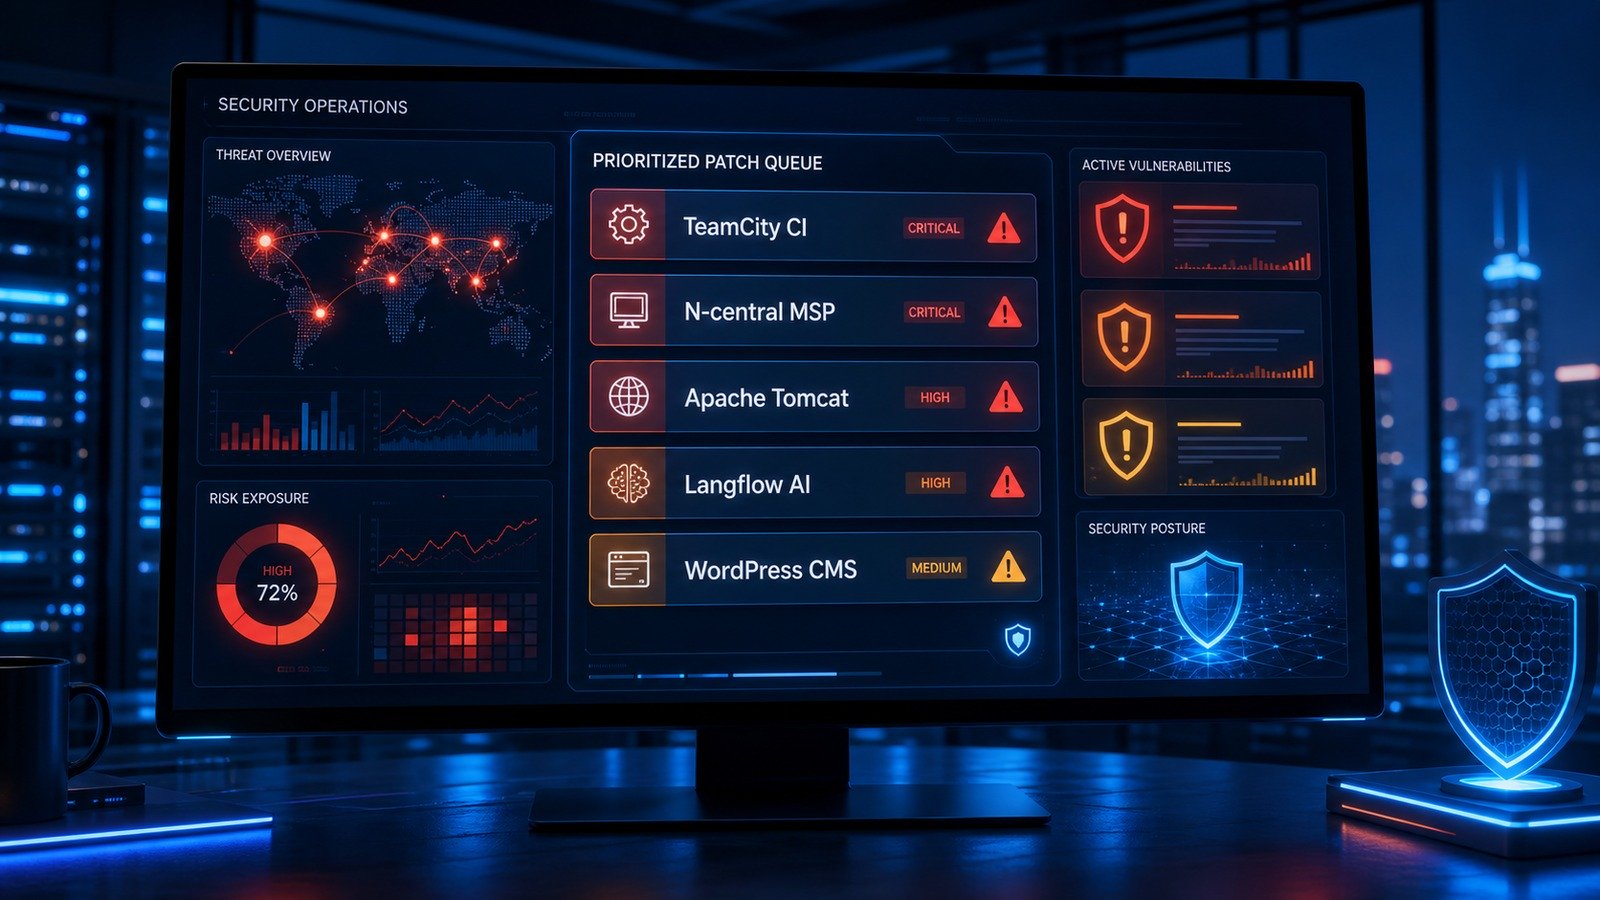
A practical small-business guide to the August 2026 CISA KEV additions, including TeamCity, N-central, Tomcat, Langflow and WordPress patch priorities.
CISA added CVE-2026-20316, a Cisco Secure Firewall Management Center hard-coded password flaw, to KEV. Here is the small-business patch and exposure checklist.
CISA warned that Russian state-supported actors are targeting Zimbra Collaboration Suite users. Here is what small businesses should check, patch, and monitor now.
CISA’s July 2026 KEV additions put SharePoint, Fortinet, Oracle, SonicWall and CMS/plugin exposure back on the small-business patch-priority list. Here is what to check first.
Shadow AI is becoming the new shadow IT problem. Learn how small businesses can inventory AI tools, review OAuth access, set data rules, and control AI SaaS risk in 2026.
July 2026 AI security news for small businesses: Langflow KEV, SharePoint, ColdFusion, remote support, UniFi OS, and how to prioritize patches without panic.